HIPAA Security Requirements can sound overwhelming when you’re running a small healthcare practice. Most owners assume HIPAA is mainly about privacy notices, consent forms, and paperwork for auditors.
In reality, the HIPAA Security Rule is much more practical than people think.
It is about protecting electronic patient information from the kinds of problems that happen every day: stolen passwords, phishing emails, lost devices, ransomware, and employees accidentally sharing information they shouldn’t.
For a 5-20 person practice, the goal is not building a hospital-grade security operation. The goal is understanding your risks and putting reasonable safeguards in place.
If you run a small or medium medical practice, the HIPAA Security Requirements you cannot afford to skip are:
Most small practices are exposed not because they ignore HIPAA entirely, but because one or more of these basics are missing.
Many practice owners view HIPAA through a compliance lens instead of a security lens.
They focus on:
Those things matter, but they are only part of the picture.
The Security Rule focuses on electronic protected health information (ePHI). That includes anything from patient records and billing systems to emails containing medical information.
The question HIPAA wants answered is simple:
“What are you doing to protect patient data from unauthorized access, loss, or compromise?”
For a practice with ten employees, the answer should be realistic, documented, and consistently followed.
HIPAA Security Requirements Start With Risk Analysis
If there is one thing every practice owner should remember, it is this:
You cannot protect what you haven’t evaluated.
HIPAA expects organizations to assess the risks to patient information. That means identifying:
This exercise often uncovers surprising issues, including:
For many small practices, a risk assessment delivers more security value than purchasing another technology tool.
One of the most commonly overlooked HIPAA Security Requirements involves access management.
In smaller offices, it is normal for employees to wear multiple hats. The danger is that access permissions often grow over time and never get reviewed.
A few simple safeguards go a long way:
For example, a receptionist may need scheduling access but not full clinical records. A billing specialist may need financial information but not every part of the patient’s chart.
Not everyone needs access to everything.
HIPAA Security Requirements Depend on People
Even the best security technology can be defeated by one convincing phishing email.
Small healthcare practices are particularly attractive targets because criminals know resources are limited and staff members are busy.
Training does not need to be complicated.
Staff should understand:
Think of training as preventive care for your practice’s cybersecurity health.
A short training session today can prevent a costly incident tomorrow.
One reason HIPAA feels frustrating is that documentation is required.
Policies, procedures, training records, and risk assessments all help demonstrate compliance.
However, documentation should reflect real-world practices.
A beautifully written policy that nobody follows does not improve security.
A practical process that employees understand and consistently use is far more valuable.
The best approach is keeping policies simple, relevant, and aligned with how your practice actually operates.
If you’re short on time, budget, or staff resources, focus here first.
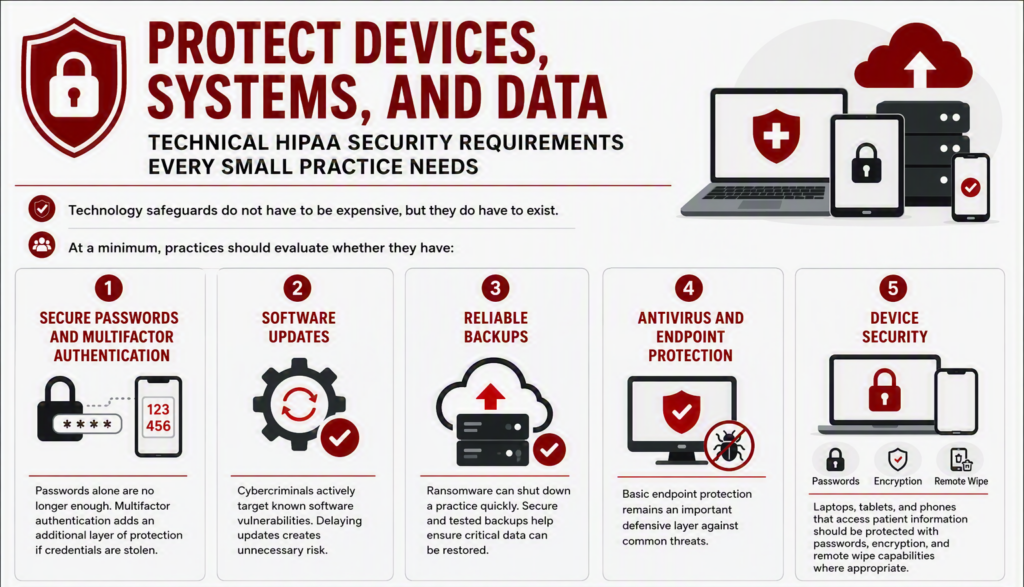
The most important HIPAA Security Requirements for a small practice are:
These four areas address the majority of the risks most small practices face every day.
They are practical, achievable, and significantly reduce exposure.
HIPAA security is not about becoming a cybersecurity expert overnight.
It’s about understanding where your practice is vulnerable and taking reasonable steps to protect patient information.
For a 5-20 person office, that means focusing on the fundamentals instead of chasing every new security trend.
When risk assessments, access controls, employee training, and technical safeguards are in place, you’re addressing the areas that matter most.
And that puts your practice in a much stronger position than many organizations that focus only on paperwork.
Not sure whether your practice has the right safeguards in place?
See where your practice actually stands in just 30 minutes. We’ll help identify gaps, prioritize the biggest risks, and give you a clear picture of what deserves attention first.
No. HIPAA expects reasonable safeguards based on your size, resources, and risks. Many small practices can significantly improve security through risk assessments, staff training, access controls, and basic technical protections.
A risk assessment is often considered the foundation. Without understanding your risks, it is difficult to implement appropriate safeguards.
Yes. Phishing remains one of the most common ways healthcare organizations experience data breaches and unauthorized access to patient information.
Yes. Anyone who interacts with patient information or practice systems should understand basic security awareness and data protection responsibilities.
At least annually, and whenever significant changes occur, such as new software implementations, office expansions, staffing changes, or evolving security threats.
This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.
Use our free Business Security Checklist to quickly identify common cybersecurity gaps and the practical steps your business can take to address them.
Enter your information below and we’ll email the free checklist directly to you.
By submitting this form, you agree to receive the requested resource and occasional communications from Hacker Watchdog. You can unsubscribe at any time. Your information will be handled in accordance with our Privacy Policy.
Learn how scammers manipulate people into giving up money, passwords, and personal information with our free Scam Defence Workshop.
Enter your information below and we’ll email the free workshop directly to you.
By submitting this form, you agree to receive the requested resource and occasional communications from Hacker Watchdog. You can unsubscribe at any time. Your information will be handled in accordance with our Privacy Policy.
Download our free Individual Online Banking Hygiene Guide and learn simple, practical steps to protect your accounts, personal information, and money from common online threats.
Enter your information below and we’ll email the free guide directly to you.
By submitting this form, you agree to receive the requested resource and occasional communications from Hacker Watchdog. You can unsubscribe at any time. Your information will be handled in accordance with our Privacy Policy.
By clicking “Accept All" button, you agree to the storing of cookies on your device to enhance site navigation, analyze site usage, and assist in our marketing efforts. Privacy Policy Cookie Policy